





A register nobody opens
Our risks live in a spreadsheet nobody has opened since the last audit.
Fix: each risk gets an owner, an approval and a yearly review.
See the risk matrixOperate · risk management software
Operate is your list of what could go wrong, the plan to fix it and the to-do list that gets it done, with a reminder whenever something is due. Aiko points out risks whose evidence says otherwise, you decide, and Swiss experts can run it for you.
Does this sound like you?
Our risks live in a spreadsheet nobody has opened since the last audit.
Fix: each risk gets an owner, an approval and a yearly review.
See the risk matrixWe agreed the treatment plan. Nobody knows who is doing what.
Fix: the plan becomes tasks, and its health shows on the risk.
See how a risk gets doneWhich version of the policy is approved, and when is it due for review?
Fix: one approval workflow, every revision kept.
See the policy workflowHow it works
You score the risk and set a target. A treatment plan links the controls and tasks that get you there, and each task done moves the plan's health.
Sample company: RISK-004, ransomware on file servers, is scored impact High by likelihood Probable, risk value 9, with the strategy Mitigate and a target of 4 after treatment. Its treatment plan links two controls, one measure and three tasks. As the three tasks are done, each with a record, the plan turns healthy, and the owner approves the risk, which sets its next review a year out.
Risks & Opportunities
Every risk carries an impact, a likelihood, a treatment strategy and a target after treatment. The matrix places them by likelihood and impact, each cell with its risk level, and one toggle switches between actual and target.
Only the owner or an administrator approves a risk. Approval sets the next review a year out, with reminders 30 days and 3 days before.Aiko in Operate
Aiko compares each risk with its evidence and proposes a new score when they disagree. A score changes only when you click Change Score, one risk at a time.
1Aiko proposes
2You confirm
3You set the pace
Ask "Create a task to renew the firewall certificates by 30 September, for Anna". Aiko drafts it, with Anna as assignee.
Admins set the highest mode for each action.
Every Aiko action goes into the Activity log.
One Aikoacross Acuna GRC. Add a module and it helps there too. How Aiko works
Business impact analysis
For each process, set how long it can be down (RTO, RPO and MTPD), describe what happens as an outage lengthens, and record the assets, people and suppliers it depends on.
SPOF Analysis lists the assets that several critical processes depend on, so you know where redundancy matters most.Tasks and Annual Plan
The Annual Plan lays recurring tasks, scheduled controls and the yearly review of every approved risk and published document on one 12-month grid, planned and done.
Recurring tasks come back on their own: finishing one creates the next. Done records who did it and when, with a record attached on the spot.Documents
A policy moves from Draft to Pending Approval, Approved and Published, with as many approvers as you need. Every change is a numbered revision you can open and compare.
Publishing sets the next review a year out, with reminders 30 days and 3 days before and when it is overdue. Export to PDF or Word.Have staff read and acknowledge it in the Staff Portal →How it connects
Risks and the BIA draw on the assets, processes and suppliers in Implement. Tasks done file records in Assure and move the health of the controls above them.
Swiss experts
CISO as a service: our experts run the risk reviews, the BIA and the policy reviews in Acuna GRC all year. You review and decide.

CEO of Abilene Group
Henri Haenni
Risk management
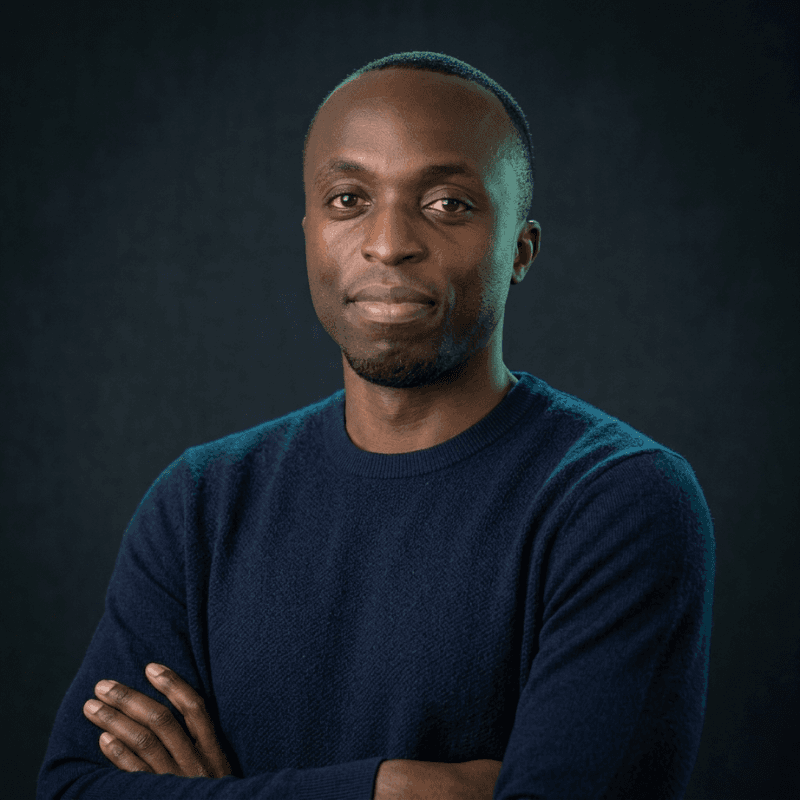
Auditing expert
Jean Munyarugerero
IS & business continuity trainerYou run the program in Acuna GRC, with Aiko.
Guidance, reviews and audit preparation with your team.
Our experts run it. You review.
Integrations
Tasks sync both ways with your ticketing tool, and connectors feed the controls and KPIs that Aiko reads when it checks a risk.
Animation: a robot arm takes data from Microsoft Entra ID, Microsoft Defender, Azure, AWS, GitHub and Jira and puts it on a belt into your workspace in Acuna, where your evidence, KPIs and security alerts stay current.
 Jira
 Entra ID
 Microsoft 365
 Defender
 CrowdStrike
 Intune
 AWS
 Azure
 GitHub
 Google Workspace
 Okta
Connectors pull security data on a schedule, and API keys let your own systems push data in. Every call is logged.
We design the integration around your setup. Every native connector we have exists because a client needed it.
Tasks sync both ways with Jira and ServiceNow. See Integrations and API
FAQ
Yes. Risks & Opportunities is one register with the same assessment, approval and review steps. Filter it by status, category, likelihood, impact, treatment or owner.
No. A catalogue of threat sources is there on day one, classified by source type and by confidentiality, integrity, availability and traceability. Edit it freely and link each threat to the assets it exposes and the risks it concerns.
Yes. Each objective has an owner, a target date and a status from Draft to Completed. Link it to requirements, controls and KPIs, and it shows the KPI target status and the health of what supports it.
Yes. Export the register to XLSX or CSV exactly as you filtered it. Documents written in Acuna GRC export to PDF or Word.
Yes. A risk links to assets, threats, processes, third parties, measures, controls and treatment plans, and to processing activities when you use Data Privacy.
In the Staff Portal add-on. You publish the document and launch the staff campaign from Operate, and staff confirm they have read it in the portal.
No. Aiko helps your team with the work, our experts add hands when you need them, and your people make the decisions.
Bring your risk register as it is. We'll show it in Operate with its matrix, treatment plans and tasks, and Aiko's view of which scores look off.
Hosted in Switzerland, the EU or the US