Swiss GRC alternative · Compared in depth

Looking for a Swiss GRC alternative? An honest comparison with Acuna GRC.

Direct answer

Acuna GRC is a Swiss GRC alternative designed around AI from the start: Aiko works natively on one data model (requirements, measures, controls, risks, suppliers, evidence and connected systems), and a person confirms under the policy your administrator sets. It suits fast-growing companies closing enterprise deals, regulated enterprises, groups with subsidiaries, MSSPs and consultancies, and teams that want the full cycle run with experts, with FINMA, NIST CSF, the EU AI Act, ISO 27001, ISO 42001, the Swiss FADP, GDPR, NIS2, DORA and 50+ frameworks in one library. It serves Swiss teams in every language region and international teams across Europe, in English, French, German and Spanish, with Swiss experts and CISO or DPO as a service in the same offer. Its risk management is built from evidence: each risk is checked against its control runs, KPIs and threats. Acuna GRC runs in Swiss or EU cloud hosting as you choose, in a private cloud or on-premises, and starts from CHF 6'390 per year with all 50+ frameworks included. Swiss GRC stays the stronger pick for Monte Carlo risk quantification, and for Zurich municipalities already covered by the canton's IKS framework contract.

Choose Acuna GRC if

  • You want AI working natively on your compliance records, with a person confirming, permissions per role and an off switch.
  • You want enterprise risk management built from evidence, with a register, treatment plans, Aiko risk analysis and one view across your entities.
  • You are closing enterprise deals that ask for ISO 27001 and security questionnaires, or running NIS2, DORA and FINMA in one record.
  • You run a head office and subsidiaries, a Microsoft-centric or hybrid stack, or many clients as an MSSP or consultancy.
  • Your teams work in English, French, German or Spanish and want Swiss experts, with CISO or DPO as a service priced in the same offer.
  • You want to see what is included before the first call: all 50+ frameworks in the published starting price.

Stay with Swiss GRC if

  • You want Monte Carlo simulation on your risk assessments (RiskQuant).
  • You are a Zurich municipality already covered by the canton’s IKS framework contract, which runs to 2029.
Book a demoSee pricing

Why do teams look for a Swiss GRC alternative?

Swiss GRC is an established Swiss GRC suite, and teams rarely look elsewhere because it is weak. The questions that do come up are how its AI is built, how long the tool takes to learn, what a full offer costs before a sales conversation, whether experts can take a role rather than only implement, which languages and regions the vendor serves, and how service providers run many clients. Each one below carries what we could verify and how Acuna GRC answers it.

  1. AI added to an established platform, or a platform built around AI

    What the evidence says

    Swiss GRC’s own history runs from the ISMS Toolbox (2005) and GRC Toolbox v1 (2012) to GRC Toolbox v3 (2020), and an AI-native platform in 2026. It presented an AI Assistant on the GRC Toolbox in July 2024 and upgraded it in April 2026. Its assistant, Grace, answers in plain language from what the signed-in person may see, names the objects it used, and proposes for accountable people to approve.[3][6][7][5]

    How Acuna GRC answers it

    Acuna GRC was designed around AI from the start. Aiko sits at the centre of operations and works natively on one data model, so its proposals rest on connected records. Your administrator sets how far it may act, per action and per role, and can switch AI off entirely: the platform keeps working. How Aiko works

  2. A tool the team can pick up quickly

    What the evidence says

    On the GRC Toolbox listing at Capterra, some reviewers mention a learning curve: it takes time to get used to the features, and some tools are hard to decipher at first.[15]

    How Acuna GRC answers it

    Acuna GRC guides the setup: the compliance roadmap lays out each framework as ordered steps and recommends the tasks, controls, measures and documents to put in place. A dedicated advisor and one month of hypercare come with every subscription, and Aiko drafts tasks and KPIs and plans missing links for a person to confirm, so no one starts from a blank page. Compliance roadmap

  3. Knowing what is included before the first call

    What the evidence says

    Swiss GRC has no published price list; pricing is quoted per project (modules, users, consulting). Some reviewers on the GRC Toolbox listing at Capterra mention that some features require buying premium modules.[1][15]

    How Acuna GRC answers it

    Acuna GRC starts from CHF 6'390 per year with all 50+ frameworks in the library, Aiko and 100+ connectors included. Add-on modules and services, from co-managed to CISO as a service, are priced in the same offer, so you see the whole program in one document. How pricing works

  4. Experts who take the role, not only the rollout

    What the evidence says

    Swiss GRC provides onboarding and support through its own consultants, with experience in risk, compliance and leadership roles, and trains certified partners who carry out implementations.[1][14]

    How Acuna GRC answers it

    Every Acuna GRC subscription includes a dedicated advisor and one month of hypercare. Beyond that, experts can co-manage or fully manage the program, act as your CISO or DPO, and prepare the audit with in-house certified lead auditors. Services

  5. A GRC partner for teams across Europe, in their language

    What the evidence says

    Swiss GRC is headquartered in Lucerne, with offices in Munich, London, Dubai, Mumbai and Pristina. Its site is offered in English, German, French, Italian and Arabic.[4][1]

    How Acuna GRC answers it

    Acuna GRC serves Swiss teams in every language region and international teams across Europe, supported in English, French, German and Spanish, with Swiss experts. Supplier questionnaires and reminder emails go out in all four languages. CISO as a service

  6. Running compliance for many clients

    What the evidence says

    Swiss GRC’s partner program trains implementation partners, who take responsibility for the technical rollout, and Swiss GRC takes on at least 20 percent of a partner’s first independent implementation.[14]

    How Acuna GRC answers it

    Acuna GRC is built for MSSPs and consultancies that deliver the program themselves: each client runs in its own organization, white label under your brand, and frameworks, templates and roadmaps are reused from one client to the next. GRC for MSSPs

Swiss GRC vs Acuna GRC: how do they compare?

Both are Swiss GRC platforms with unlimited users, cloud, private cloud and on-premises deployment, internal controls, TPRM and data protection. Swiss GRC adds Monte Carlo risk quantification, process and contract management, and an AI assistant added to a platform that has grown since 2005: it is the established tool. Acuna GRC is the newer platform, built around AI on one data model, that teams switch to; it scores risks from their evidence, includes all 50+ frameworks in its starting price, and sells experts who can take the CISO or DPO role. The last column says honestly who has the edge on each line.

Swiss GRC vs Acuna GRC comparison, as of November 2026
CriterionAcuna GRCSwiss GRCEdge
Target marketFast-growing companies closing enterprise deals, regulated enterprises, groups with subsidiaries, MSSPs and consultancies, teams that want the full cycle run with experts; FINMA, NIST CSF, the EU AI Act, ISO 27001, ISO 42001, the Swiss FADP, GDPR, NIS2, DORA and 50+ frameworks in one libraryOrganizations "from all industries"; head office in Lucerne with offices in Germany, the UK, the UAE, India and Kosovo; public buyers through tenders such as the Canton of Zurich IKS framework[1][4][16]DependsSwiss GRC: broad enterprise suite and public tenders; Acuna GRC: growing and regulated companies, groups and providers
AI architectureDesigned around AI: Aiko works natively on one data model (requirements, measures, controls, risks, suppliers, evidence, connected systems), answers from records the person may open, drafts tasks and KPIs, links records in bulk runs and proposes risk scores from their evidence; a person confirms under admin-set policy; AI permissions per role and per action; AI can be switched off and the platform keeps workingAn AI assistant, now named Grace, on a platform whose timeline runs from 2005 (ISMS Toolbox) to GRC Toolbox v3 (2020); assistant presented on the GRC Toolbox in 2024, upgraded in April 2026; answers from what the signed-in person may see, names the objects it used, proposes for people to approve; AI GRC module[3][6][7][5]Acuna GRCPlatform built around AI, not AI added to it
Hosting and deploymentSwiss or EU cloud hosting as you choose, private cloud or on-premisesSaaS, private cloud or on-premise; SaaS data location Switzerland (Microsoft Azure)[1][2]BothBoth offer Swiss cloud, private cloud and on-premises
Enterprise risk managementRisk register with impact, likelihood, inherent and residual risk and a heatmap coloured by your risk appetite; treatment plans whose health rolls up from their controls; Aiko risk analysis lists each control run, KPI and threat with its source and date and proposes a score from that evidence; open risks across subsidiaries in the group viewRisk management module; RiskQuant runs Monte Carlo simulation on existing assessment data[2][9]Acuna GRCRisks scored from their evidence, across entities; Swiss GRC adds Monte Carlo
Breadth of the suiteCore GRC (Comply, Implement, Operate, Assure) with risks, internal controls, evidence, audits and documents; add-on modules for TPRM, Data Privacy, Trust Center, AI Governance, Group management, Vulnerability management, Staff portal and Cookie managerRisk management, RiskQuant (Monte Carlo), compliance, information security, TPRM, Third-Party Intelligence, internal controls, business continuity, data protection, AI GRC, internal audit, operational resilience, plus process management (BPM) and contract management[2][9][11]DependsSwiss GRC adds BPM, contracts and Monte Carlo; Acuna GRC goes deeper on risk, controls, evidence, TPRM, Trust Center, privacy, AI governance and groups
Frameworks50+ in the library, all included: NIS2, DORA, FINMA, Swiss FADP, GDPR, EU AI Act, ISO 27001, ISO 42001, SOC 2 and more; custom frameworks by CSVNamed on its site: DORA, NIS2, the Cyber Resilience Act, GDPR, the Swiss FADP, the EU AI Act, ISO/IEC 42001 and NIST AI RMF; FINMA is not named on the pages we opened[2][8]DependsAcuna GRC: FINMA and 50+ in one shared library
Third-party risk (TPRM)Supplier Shield: supplier register with your own exposure model, questionnaires by campaign through a supplier portal, a 1 to 3 shield rating, a daily A to F OSINT grade, and Aiko drafting or evaluating answers for a person to confirmDedicated TPRM module: central inventory, risk-tiered reassessments, questionnaires with reminders and escalation, DORA register of information; Third-Party Intelligence monitors third parties continuously for sanctions, PEP and adverse media[12][13]BothBoth run full TPRM
Controls, evidence and integrationsConnectors record control passes and fails and KPI values every 4 hours; 100+ connectors, and we build the connectors your stack needs; Jira and ServiceNow two-way task sync; API v1, webhooks, scheduled CSV importsInternal controls run, evidenced and assessed continuously; open REST API, single sign-on, Microsoft Office integration, adapters and connectors[10][2]BothBoth connect; Acuna GRC builds connectors to your stack
PricingPublished: from CHF 6'390 per year, per organization, all 50+ frameworks, Aiko and 100+ connectors included; add-on modules and services priced in the same offer; unlimited usersNo published price list; pricing is quoted per project (modules, users, consulting)[1]Acuna GRCWhat is included is visible in one offer
ServicesDedicated advisor and one month of hypercare included; co-managed or fully managed; CISO and DPO as a service; in-house certified lead auditorsOnboarding and support by its own consultants; certified implementation partners[1][14]Acuna GRCOutsourced CISO and DPO roles
Groups, MSSPs and partnersGroup management for a head office and its subsidiaries; each MSSP client in its own organization, white label under your brandPartner program for certified implementation partners, with Swiss GRC on at least 20 percent of a partner’s first rollout[14]Acuna GRCMulti-client white label
Local presence and languagesSwiss teams in every language region and international teams across Europe; supported in English, French, German and Spanish, with Swiss experts; supplier questionnaires and reminder emails in all fourHead office in Lucerne; website in English, German, French, Italian and Arabic[4][1]Acuna GRCSwiss experts, supported in four languages across Europe

Swiss GRC facts as of November 2026, from the pages in the sources below. Acuna GRC security documentation, and how Aiko handles data, are in the Acuna Trust Center.

TPRM: every supplier with its risk level, its assessment rating and a daily public-exposure grade, on the same records as your controls.
Trust Center: questionnaire answers are drafted only from facts you approved, each shows what it was built from, and an answer citing a draft document is flagged before anyone approves it.

How is AI built into Swiss GRC and Acuna GRC?

Swiss GRC added AI to an established platform: Grace, its assistant, answers in plain language from what the signed-in person may see and proposes for people to approve, on a platform whose timeline runs from the ISMS Toolbox (2005) to GRC Toolbox v3 (2020). Acuna GRC was designed around AI from the start. Aiko sits at the centre of operations and works natively on one data model, so every answer and proposal rests on connected records, and your administrator decides how far it may go.

One data model, connected records

Aiko works on the same records as every module: requirements, measures, controls, risks, suppliers, evidence and the results of connected systems. Each answer carries a badge naming the module it drew on, and a risk analysis lists every control run, KPI and threat with its source and date.

A person confirms, under your policy

Aiko prepares each action on a card. For each action your administrator sets the highest mode anyone may use: Suggest only, Ask me first or Do it and tell me. A risk score change always asks first, and every action is kept in the Activity log for 12 months.

Permissions carry over, per role

Aiko answers only from records the person could open, and says so when an access profile hides a kind of record. Access profiles decide which of Aiko’s skills load and who may trigger AI evaluation of supplier assessments.

Switch it off, keep working

One switch turns AI features off for the whole organization. When it is off, Aiko stops reading or proposing anything, and every module keeps working as before.

How Aiko works

Questions to ask any GRC vendor about its AI

  1. Which records can the AI read, and are they the same data model as your controls and evidence?
  2. Do a person’s permissions carry over to what the AI can see and do?
  3. Can AI be limited per role and per action, or switched off for the whole organization?
  4. Does a person confirm each change, and who sets that policy?
  5. Is every AI action logged, and for how long?
  6. Does the platform keep working with AI switched off?

How Aiko handles data is documented in the Acuna Trust Center.

One data model: each Aiko answer names the module it drew on, from the same records your team works in.
Your policy: one switch for AI in the whole organization, and the highest mode allowed for each action.

What does Acuna GRC look like in under two minutes?

The Acuna GRC film shows the platform in 1 minute 39 seconds: why GRC keeps getting harder, cross-framework mapping and dashboards, and Aiko working on your compliance and risk data. It plays only when you click.

Watch the film · 1:39

Acuna GRC home

Acuna GRC in 1 minute 39 seconds: one connected compliance platform with 50+ frameworks, cross-framework control mapping, risk, TPRM, privacy, audit and AI governance, GRC dashboards, and Aiko, the AI assistant built into every page.

Chapters

  1. Why GRC and compliance are getting harder
  2. Meet Acuna GRC
  3. Cross-framework mapping and GRC dashboards
  4. Aiko: AI for compliance and risk
  5. Results: less manual work, faster compliance
Watch on YouTube

How much does Swiss GRC cost compared to Acuna GRC?

Swiss GRC has no published price list; pricing is quoted per project (modules, users, consulting). Acuna GRC starts from CHF 6'390 per year for one organization, with all 50+ frameworks, Aiko and 100+ connectors included, and prices add-on modules and services in the same offer. Ask both for the same scope in writing and compare it over three years.

What Acuna GRC costs

FromCHF 6'390per year

Published, per organization, with unlimited users. Add-on modules and services are priced in the same offer.

Included

  • Core GRC: Comply, Implement, Operate and Assure
  • All 50+ frameworks in the library
  • Aiko, the AI assistant
  • Integrations and API, 100+ connectors
  • Administration and security
  • A dedicated advisor and one month of hypercare

Shown in your local currency where we publish one.

See pricing and what is included

What Swiss GRC costs

Quoted, not published

No published price list; pricing is quoted per project (modules, users, consulting).[1]

Ask for in writing

  • Which modules the quote covers, and what each added module costs
  • Onboarding, consulting and training fees
  • Ongoing support and renewal terms
  • The price of your deployment: SaaS, private cloud or on-premise

What to compare in a three-year view

Modules in scope

List the modules your program needs (TPRM, data protection, internal control, AI governance) and ask each vendor to price the same list.

Services

Ask what onboarding, consulting, ongoing support and expert roles such as CISO or DPO as a service cost with each vendor.

Who runs the program

Count the internal hours to keep controls, suppliers and evidence current, and decide whether your team, the vendor’s experts or both will do it.

Deployment

Swiss cloud, EU cloud, private cloud or on-premises: both vendors offer more than one option, and the choice can change the price.

Which GRC software in Switzerland covers FINMA, NIS2, DORA and the Swiss FADP?

Both cover the main Swiss and EU obligations. Swiss GRC names DORA, NIS2, the Cyber Resilience Act, GDPR, the Swiss FADP and the EU AI Act on its site, with a DORA register of information in its TPRM module. Acuna GRC keeps FINMA, NIS2, DORA, the Swiss FADP, GDPR and the EU AI Act in one library of 50+ frameworks, all included, where they share measures, controls and records with ISO 27001.

FINMA, NIS2, DORA, Swiss FADP and EU AI Act: Acuna GRC vs Swiss GRC, as of November 2026
RegulationAcuna GRCSwiss GRC
FINMAIn the library, adopted next to DORA, with business impact analysis and providers ratedFINMA compliance softwareNot named on the Swiss GRC pages we opened[2]
NIS2In the library, mapped to shared measures; Group Compliance shows every entity in scopeNIS2 explainedNIS2 compliance softwareNamed on its platform page (NIS2 Directive)[2]
DORAIn the library, with the third-party register, business impact analysis and incident timelines on the same dataDORA explainedDORA compliance softwareNamed on its platform page; TPRM keeps a register of information on critical outsourcings (DORA Art. 28 to 30)[2][12]
Swiss FADPIn the library; with Data Privacy it drives legal bases, the ROPA and DPIAsSwiss FADP explainedFADP compliance softwareNamed with GDPR; Data Protection module[2]
EU AI ActAI Governance module: register of AI systems, impact assessments, human oversight, incidents and a contestation channelEU AI Act explainedAI GovernanceAI GRC module: EU AI Act risk classes and roles, ISO/IEC 42001 and NIST AI RMF[8]
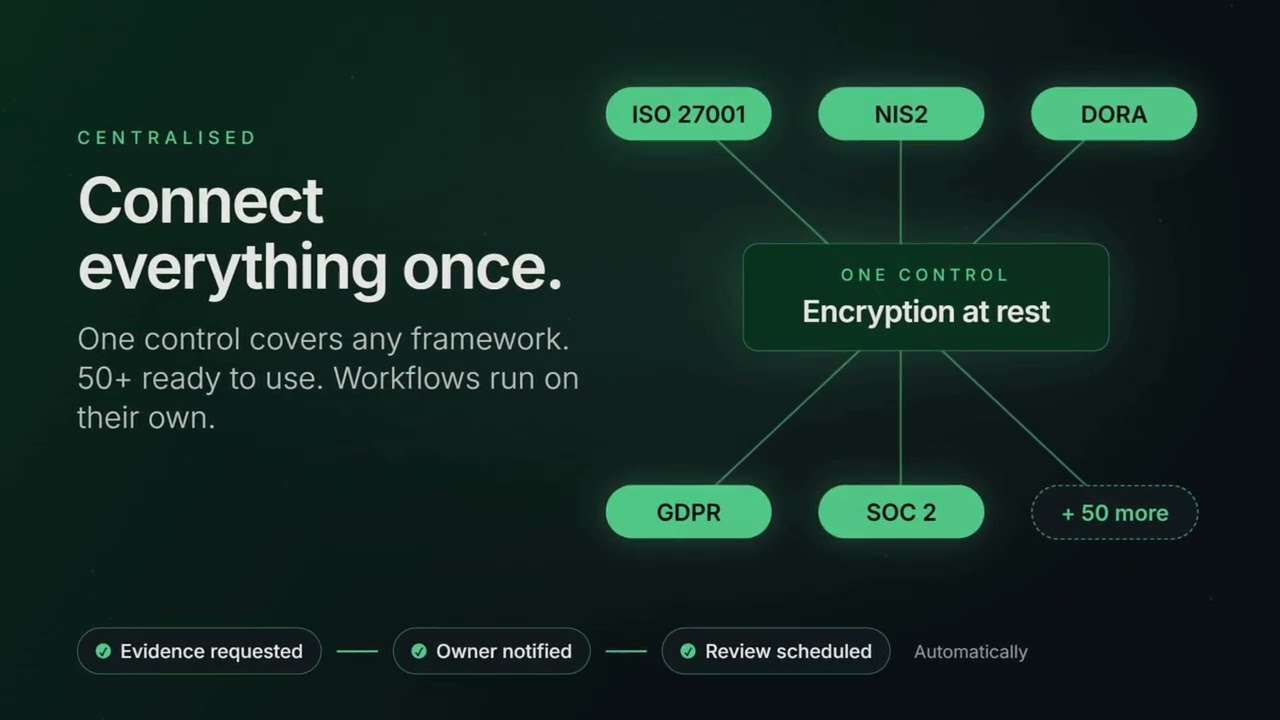
One control library across frameworks: each measure is linked to every requirement it meets, so a framework you add reuses the work already done.

How does Acuna GRC make evidence auditors can trust?

Acuna GRC is workflow-first. Every requirement is met by a measure, verified by a control and carried out through tasks, and each completion records who did it, when, and the record that proves it. Health is computed from that chain, never typed in.

Records from the work itself

Completing a task or a control execution creates or links a typed, dated record that names who did the work. A checklist run is signed item by item and files its own PDF record.

Approvals and reviews built in

Risks, documents and exceptions move through approval workflows with a history of every state change. Yearly reviews come with reminders 30 days and 3 days before, and when overdue.

Evidence from the browser

The Acuna browser extension (Chrome and Edge) shows your tasks, controls, approvals, reviews and deadlines in a popup or side panel. A screenshot you paste as evidence is stamped with the UTC date and time and your Acuna email before it is sent.

Extension privacy notice

Connector results where they fit

Connectors record control passes and fails and KPI values every 4 hours. Where no connector understands your stack, a control is judged on completed records or a checklist instead, so every control still produces evidence.

Evidence: a control names its owner, how it is judged and when it is due, and each run is signed and filed as a record.
Approvals: a policy is published only after its approvers sign, and every change is a numbered revision.

When is Acuna GRC the better choice?

Acuna GRC is the better choice than Swiss GRC for fast-growing companies closing enterprise deals that ask for ISO 27001 and security questionnaires, regulated EU enterprises running NIS2 and DORA in one record, groups with a head office and subsidiaries, MSSPs and consultancies, organizations that want the full cycle run with experts, risk teams that want risks scored from their evidence, Microsoft-centric and hybrid IT teams, teams across Europe working in English, French, German or Spanish, and teams that want AI working natively on their compliance records.

Buyers for whom Acuna GRC is the better choice than Swiss GRC, as of November 2026
BuyerBetter choiceWhy
Fast-growing companies closing enterprise deals that ask for ISO 27001 and security questionnairesAcuna GRCThe Trust Center, questionnaire drafts from approved library facts and one audit log answer due diligence requests from one set of records, and the compliance roadmap sets up the program in one approval step.Trust CenterCompliance roadmapISO 27001
Regulated EU enterprises that must run NIS2 and DORA obligations in one recordAcuna GRCIncident reports, supplier assessments and exceptions sit together with shared owners and dates, and ISO 27001 measures link to the same controls.NIS2DORATPRMMeasures and controls
Enterprises with a head office and subsidiaries that want one view across entitiesAcuna GRCGroup management and group dashboards cover the head office and its subsidiaries, while each entity keeps its own records.Group management
MSSPs and consultancies running compliance for several clientsAcuna GRCClient management and white-label portals under the provider’s own brand, with frameworks, templates and roadmaps reused from client to client.GRC for MSSPsPartner program
Organizations that want the full compliance cycle run with experts on the same recordsAcuna GRCCompliance roadmap, one control library across more than 50 frameworks, in-house certified lead auditors, and CISO and DPO services that run or support any part of the cycle.ServicesCISO as a serviceDPO as a service
Risk and internal control teams that want risks scored from their evidenceAcuna GRCEach risk carries inherent and residual values and a treatment plan whose health rolls up from its controls; controls have owners, schedules and signed runs on record; Aiko checks whether a score still matches its evidence and proposes a new one for the risk owner to confirm; the group view shows open risks in every subsidiary.Risk managementAiko
Microsoft-centric and hybrid IT teamsAcuna GRCEntra ID, Intune, Defender, Sentinel and Secure Score connectors, sign-in with Microsoft, Teams summaries, and scheduled imports from on-premise systems.Integrations and API
Teams across Europe working in English, French, German or SpanishAcuna GRCAcuna GRC serves Swiss teams in every language region and international teams across Europe in all four languages, with Swiss experts, and its starting price includes all 50+ frameworks, so a lean team can run FINMA, the Swiss FADP, NIS2 and ISO 27001 with experts close by.PricingSwiss FADP
Teams that want AI working natively on their compliance recordsAcuna GRCAiko is built into every page and works on the same records as every module, so it answers from your own data, drafts tasks, links controls to measures in bulk runs and proposes a new risk score with the evidence behind it. A person confirms, under the policy your administrator sets, AI permissions follow each role, and AI can be switched off entirely.AikoAI Governance
Aiko works on the same records as every module: it gathers a risk’s control runs, KPIs, vulnerable items and threats, each with its source and date, and proposes a new score for a person to confirm.
Group management: one view across the head office and its subsidiaries, worst first, while each entity keeps its own records.

When is Swiss GRC the better choice?

Choose Swiss GRC when you want Monte Carlo simulation on your risk assessments, or when you are a Zurich municipality already covered by the canton’s IKS framework contract. These are real strengths:

Buyers for whom Swiss GRC is the better choice than Acuna GRC, as of November 2026
BuyerBetter choiceWhy
Risk teams that want Monte Carlo risk quantificationSwiss GRCRiskQuant runs Monte Carlo simulation on existing assessment data, inside the same suite as Swiss GRC’s risk management.[9][2]
Municipalities and cities in the canton of Zurich already covered by the IKS framework contractSwiss GRCSwiss GRC AG won the canton’s framework contract for internal control (IKS) software for its municipalities and cities, as SaaS from 2025 to 2029 with a three-year option, so it is the procurement route already in place. Acuna GRC also runs internal control systems (IKS/ICS), with owners, tests and evidence in the same records, and can be brought in easily.[16]

What are the other Swiss GRC alternatives?

Which Swiss GRC alternative fits depends on the buyer. Drata and Vanta suit SOC 2-first companies, Kertos German and EU companies that want a German vendor with experts, and Acuna GRC Swiss and EU regulated firms, groups, MSSPs and teams that want AI built into one data model.

Swiss GRC alternatives and who each suits, as described on each vendor’s site, November 2026
PlatformWho it suits
DrataSOC 2-first companies; 30+ pre-built frameworks including NIS 2 and DORA, with FINMA and the Swiss FADP not on its list.[17]
VantaStartups to enterprises that want 400+ integrations and 35+ frameworks, starting from SOC 2 and ISO 27001.[18]
KertosScale-ups and mid-sized companies that want a platform made in Germany with certified experts, covering NIS2, GDPR, the EU AI Act, ISO 27001, TISAX and C5.[19]
Acuna GRCFast-growing companies closing enterprise deals, regulated EU enterprises under NIS2 and DORA, groups, MSSPs and consultancies, and teams across Europe working in English, French, German or Spanish, with FINMA, the Swiss FADP and 50+ frameworks included and Aiko working on one data model.

If you are comparing SOC 2-first tools too, read Acuna GRC vs Drata.

How do you move from Swiss GRC to Acuna GRC?

You move in four steps: bring in what you have, map it once across frameworks, connect your systems, then run. Your dedicated advisor plans the order with you, and how long it takes depends on how many frameworks, modules and entities you bring.

  1. Bring it inData Import wizard

    Export your registers from Swiss GRC in the formats your setup allows, then import assets, risks, third parties, staff and documents from CSV or Excel, mapped and validated first.

  2. Map onceShared measures

    Adopt your frameworks and the reference measures that cover several at once; Mapping lists every gap.

  3. Connect100+ connectors

    Turn on the connectors you use. A missing one is built on request, around your stack.

  4. RunTasks, approvals, records

    Recurring tasks and controls start producing records, and the roadmap shows what is left.

Run it yourself, or with CISO and DPO as a service

Do it yourself

Your team runs Acuna GRC, with a dedicated advisor and one month of hypercare included.

Done with you

Co-managed: our experts guide, review and prepare the audit with your team.

Done for you

Fully managed: our experts run the program, you review and decide.

CISO or DPO as a service

A named Swiss expert in the role for as long as you need.

See services

Connect: each connector feeds KPI measurements and control passes or fails every 4 hours, so continuous monitoring starts the day you switch it on.

Integrations

Does Acuna GRC connect to the tools we already use? Yes, 100+ connectors.

Connectors pull security data from your identity, endpoint, cloud, code and HR tools on a schedule, so evidence stays current without screenshots.

  • Entra ID
  • Okta
  • Google Workspace
  • Defender
  • CrowdStrike
  • Intune
  • AWS
  • Azure
  • GitHub
  • Jira
  • 100+ connectors in all

Missing a connector? We build it. We design the integration around your setup. Every native connector we have exists because a client needed it.

See Integrations and API →

What does running Acuna GRC look like?

Four example scenarios show how different organizations would run in Acuna GRC, using documented features only.

Example scenario

A Swiss financial intermediary preparing for FINMA and DORA

One compliance lead, a busy IT team and an ICT provider list nobody fully trusts.

  1. Adopt FINMA and DORA together in Comply; one measure counts for every requirement it meets.
  2. Record ICT providers as third parties and link them to processes in the business impact analysis, with RTO and RPO.
  3. Log incidents as issues with a dated timeline, and generate the management report from Assure.

92%less time preparing for audits, with controls mapped across frameworks

FINMADORA

Example scenario

A mid-sized company in Vaud with a CISO as a service

No in-house CISO, an ISO 27001 request from a large customer and personal data under the Swiss FADP.

  1. A named CISO from Acuna GRC’s experts takes the role and runs the compliance roadmap with the team.
  2. ISO 27001 and the Swiss FADP are adopted together; Data Privacy keeps the ROPA and DPIAs on the same records.
  3. Aiko lists the controls without a measure and plans the missing links for the CISO to confirm.

Up to 80%less manual work

CISO as a serviceSwiss FADP

Example scenario

A group with five subsidiaries on NIS2

A head office accountable for NIS2 across entities that each run their own way.

  1. The head office pushes a managed access profile and shared suppliers to every subsidiary.
  2. A group KPI is measured in each subsidiary and rolled up nightly.
  3. Group Compliance ranks the entities worst first; the head office evaluates one and dispatches the findings as issues.

3xmore productive: controls are checked automatically, so fixes start sooner

Group managementNIS2

Example scenario

An MSSP running 20 clients

A small team delivering the same compliance work to many clients.

  1. Each client runs in its own organization, under the MSSP’s brand.
  2. Frameworks, templates and roadmaps are reused from one client to the next.
  3. Client security questionnaires are answered from an approved answers library in the Trust Center.

10xfaster answers to customer security questions

MSSPsTrust Center

These are example scenarios, not customer stories, and they name no customer. The figures are Acuna GRC’s published platform figures, not results of these examples.

Swiss GRC alternatives: common questions

Sources

Every Swiss GRC fact on this page comes from one of these pages, opened on 5 November 2026.

  1. Swiss GRC, “Swiss GRC: Integrated GRC. One intelligent platform.”, accessed 5 Nov 2026.
  2. Swiss GRC, “GRC Software: All Disciplines on One Platform”, accessed 5 Nov 2026.
  3. Swiss GRC, “Trusted GRC Solutions for Modern Businesses (history)”, accessed 5 Nov 2026.
  4. Swiss GRC, “Contact”, accessed 5 Nov 2026.
  5. Swiss GRC, “AI Assistant: Enhance GRC with Automation and Insights”, accessed 5 Nov 2026.
  6. Startupticker, “GRC in the Age of AI: 2024 Insights and AI Capabilities of the GRC Toolbox”, event of 9 Jul 2024.
  7. Security MEA, “Swiss GRC Enhances GRC Platform with AI, Risk Modelling & DORA Tools”, 3 Apr 2026.
  8. Swiss GRC, “AI GRC for Effective AI Risk Management”, accessed 5 Nov 2026.
  9. Swiss GRC, “RiskQuant: Monte Carlo risk simulation”, accessed 5 Nov 2026.
  10. Swiss GRC, “ICS Software for Internal Controls”, accessed 5 Nov 2026.
  11. Swiss GRC, “BPM Software for Business Process Management”, accessed 5 Nov 2026.
  12. Swiss GRC, “TPRM for Greater Control Over Third-Party Risks”, accessed 5 Nov 2026.
  13. Swiss GRC, “Third-Party Intelligence Center for AI Screening”, accessed 5 Nov 2026.
  14. Swiss GRC, “Partner”, accessed 5 Nov 2026.
  15. Capterra Switzerland, “GRC Toolbox”, accessed 5 Nov 2026.
  16. Tenderlift, from simap.ch, “Software für ein internes Kontrollsystem (IKS) für die Gemeinden und Städte des Kantons Zürich (simap 39f22c05)”, accessed 5 Nov 2026.
  17. Drata, “Frameworks”, accessed 5 Nov 2026.
  18. Vanta, “Vanta”, accessed 5 Nov 2026.
  19. Kertos, “Kertos”, accessed 5 Nov 2026.

See it on your program

Compare it on your own frameworks

Show us the frameworks, entities and modules you run on Swiss GRC today. We will show you how the same program runs in Acuna GRC, with Aiko on your records, and what it costs.