





The regulator and our clients ask who owns security. Nobody does, full time.
Fix: Our Swiss experts take the role on demand, and every review they run is kept in Acuna GRC, where you can see it.
Meet the expertsCISO as a service
CISO as a service: our experts run the risk reviews, the BIA and the policy reviews in Acuna GRC all year. You review and decide. A virtual CISO, with all the work where you can see it.
Does this sound like you?
Regulators, clients and auditors expect someone to own information security all year. Many companies cannot hire a full-time CISO, or theirs has too much on the plate.
The regulator and our clients ask who owns security. Nobody does, full time.
Fix: Our Swiss experts take the role on demand, and every review they run is kept in Acuna GRC, where you can see it.
Meet the expertsThe risk register was last reviewed for the audit.
Fix: Risk reviews run all year: each approved risk has a yearly review, reminded to its owner and confirmed in Operate.
See risk reviewsWe can’t hire a CISO, and one person would not cover everything.
Fix: You work with experts with different strengths: risk and governance, business continuity and auditing.
See what it coversWhat it covers
Our experts run the risk reviews, the BIA and the policy reviews in Operate, follow up remediation and prepare your audits in Assure. Every step is recorded in Acuna GRC, so nothing lives in a report you only see once a quarter.
Our experts prepare the risk assessments with your risk owners, who approve them, and run the treatment plans. Each approved risk gets a yearly review: the owner is reminded 30 days before, and Confirm review moves the date a year forward.
See Operate →Our experts run the business impact analysis with you: RTO, RPO and MTPD per process, and a SPOF analysis that lists the assets several critical processes depend on, so you know where redundancy matters most.
See the BIA in Operate →Our experts draft or update your policies and send them for approval. Publishing sets the next review date, and the yearly review of each published document sits on the annual plan, so no policy quietly ages.
See documents in Operate →Our experts own the remediation follow-up and report to you. Each vulnerability becomes one issue with an owner and a due date set from its severity, and the owner is reminded before it is due. You decide what gets fixed and what gets accepted.
See Vulnerability management →Our experts prepare it with you in Assure: the records the auditor will ask for, the internal audit, the issues and corrective actions, and the management report. Your certification audit stays independent.
See Assure →Aiko at your pace
Ask Aiko whether a risk still matches its evidence. It gathers the last control executions, the KPIs against target and the open vulnerable items on the risk’s assets, each with its source and date.
1Aiko proposes
2You confirm
3You set the pace
Aiko can propose a new impact and likelihood for one risk, with the evidence on the card. Nothing changes until someone clicks Change Score.
Admins set the highest mode for each action.
Every Aiko action goes into the Activity log.
One Aikoacross Acuna GRC. Add a module and it helps there too. How Aiko works
Swiss experts
Extra hands to stay compliant all year: our experts run the security work inside Acuna GRC, with you. You keep the decisions.


CEO of Abilene Group
Henri Haenni
Business continuity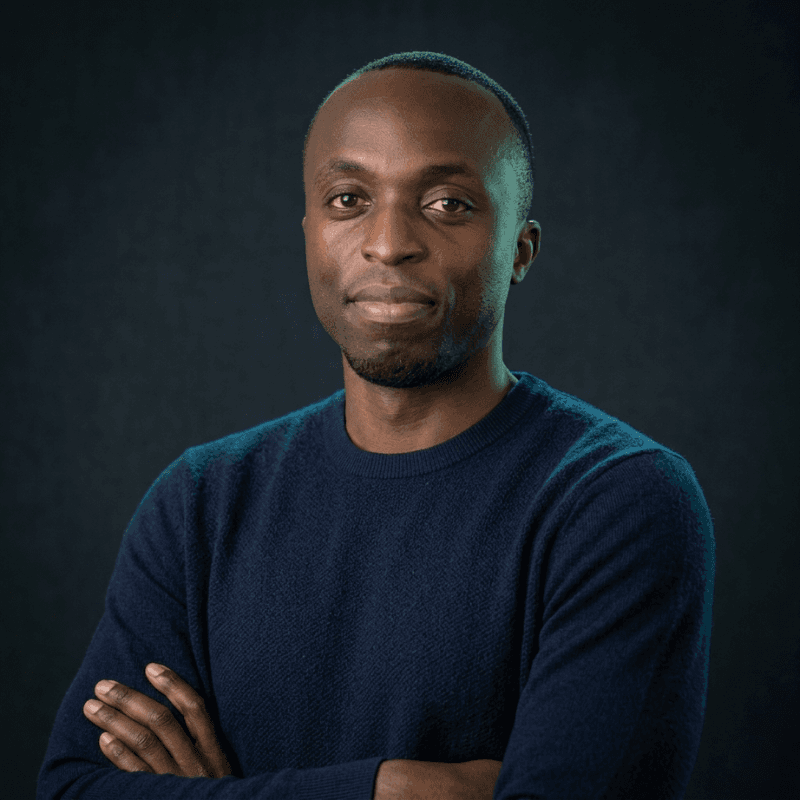
Auditing expert
Jean Munyarugerero
Management systems auditorYou run the program in Acuna GRC, with Aiko.
Guidance, reviews and audit preparation with your team.
Our experts run it. You review.
Integrations
Connectors pull data from your identity, device and cloud tools on a schedule and record it as KPI measurements or control executions, so your expert and your team read the same numbers.
Animation: a robot arm takes data from Microsoft Entra ID, Microsoft Defender, Azure, AWS, GitHub and Jira and puts it on a belt into your workspace in Acuna, where your evidence, KPIs and security alerts stay current.
 Entra ID
 Entra Access Reviews
 Okta
 Intune
 Defender
 CrowdStrike
 Jamf Pro
 AWS
 Azure
 Microsoft 365
 GitHub
 KnowBe4
 Acronis
 Jira
Connectors pull security data on a schedule, and API keys let your own systems push data in. Every call is logged.
We design the integration around your setup. Every native connector we have exists because a client needed it.
Tasks sync both ways with Jira and ServiceNow. See Integrations and API
How it connects
Risk reviews, the BIA and policies run in Operate. Implement holds the controls and owners, Assure the records and reports, and Comply your frameworks.
FAQ
Yes. Virtual CISO, fractional CISO, external CISO (externer CISO) and CISO as a service all describe a security lead you do not employ full time.
Then Done with you fits better: our experts give your CISO extra hands, in the same Acuna GRC workspace. Acuna GRC for CISOs
You do. Our experts run the work and prepare the decisions. Your risk owners approve the risks, your approvers sign off the policies, and your team decides what gets fixed.
It depends on your scope: the frameworks you run, the number of entities and sites, how often reviews fall due and how much of the work our experts take on. Tell us your scope and we size the service with you.
It supports it but does not replace it. NIS2 asks your management body to approve the cybersecurity risk-management measures, oversee them and follow training. Our experts prepare the risk reviews, policies and reports your management approves and oversees, and the decisions stay with them. NIS2 explained
No. Our experts help you prepare, and your certification audit stays independent: only an accredited certification body can certify you. Certification audit preparation
The frameworks you adopt in Comply, such as ISO 27001, NIS2, DORA, FINMA requirements or the NIST CSF. NIS2 compliance software
The service runs inside Acuna GRC, so you see every review, risk and policy as it happens, not in a report at the end of the quarter.
Not this page: see Acuna GRC for MSSPs, built for firms that deliver security and compliance services to their clients. Acuna GRC for MSSPs
In Switzerland, the EU or the US, as you choose.
Tell us your frameworks and where you stand. We show you how our experts would run the work in Acuna GRC, and what stays with your team.
Hosted in Switzerland, the EU or the US