The audit rush
“Our ISO 27001 audit is in 60 days, and our evidence is scattered across 40 Excel tabs and Jira tickets.”
Fix: your evidence in one place, each item linked to its control.
Assure →AI-native GRC, built in Switzerland
The most flexible all-in-one GRC platform: agentic AI that earns your trust step by step, and Swiss experts as extra hands to keep you compliant all year.
Sample company. The assistant proposes, you confirm.
Does this sound like you?
You answer for the program. But the evidence sits in spreadsheets, tickets and inboxes, the experts you need are hard to find, and the board wants answers now.
“Our ISO 27001 audit is in 60 days, and our evidence is scattered across 40 Excel tabs and Jira tickets.”
Fix: your evidence in one place, each item linked to its control.
Assure →“NIS2 and the AI Act apply to us now, and we don't know how to turn the legal text into IT tasks.”
Fix: see how Acuna GRC turns legal text into work.
Implement →“Big clients keep sending us 200-question security assessments, and it slows our sales by weeks.”
Fix: draft answers from your approved answers library, and our experts can help you review them.
Trust Center →“We mapped our risks last year. Nothing has been updated since.”
Fix: each risk sits next to the controls, KPIs and threats behind it, with their dates.
Operate →The platform
Requirements, measures, tasks and evidence are already linked, so you can follow the chain from a legal text to its proof.
Plan
Run
Prove
AI & experts
One control, many frameworks. Do the work once.
"The use of multi-factor authentication or continuous authentication solutions…"
 Entra IDLast run 08:40
 DefenderLast run 08:35
 GitHubLast run 07:50
 AWSLast run 06:00Entra IDMFA coverage → CTRL-021 MFA for adminsToday 08:40DefenderOpen alerts → CTRL-030 Activity monitoringToday 08:35GitHubBranch protection → CTRL-033 Secure codingToday 07:50AWSBucket encryption → CTRL-024 Encrypted storageToday 06:00Entra IDStale admin accounts → CTRL-018 Privileged accessToday 08:40
Which measures should CTRL-012 be linked to?
CTRL-012 Encryption at rest has one measure. Two more already cover it:
Why: both cover ISO A.8.24 and NIS2 21(2)(h), and AWS already sends their evidence.
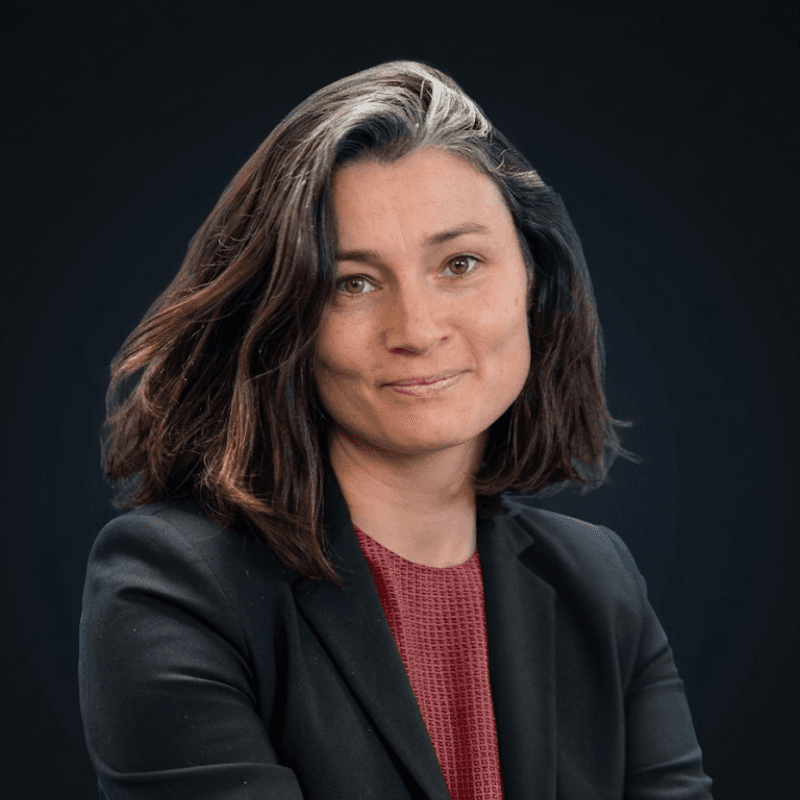 Your Acuna expertBénédicte SévinGRC Consulting team leaderISO 27001 Lead ImplementerNext check-in: Tue 10:00Your expert does
Program status: On track for the ISO 27001 audit on 2 Dec
You review and decide. We run it.
Measured across Acuna GRC customers. See the frameworks we cover →
Supplier questionnaires and a daily A to F grade, with draft answers from the supplier's own files.
Learn more →Module · 02 / 09Processing activities, data flows, DPIAs, requests and breaches, with a public privacy portal.
Learn more →Module · 03 / 09A cookie banner on your websites and a record of each visitor's choice, as part of Data Privacy.
Learn more →Module · 04 / 09Answer RFPs and security questionnaires from your approved answers, and share a public trust page with gated documents.
Learn more →Module · 05 / 09A register of the AI systems you build, buy or deploy, with impact assessments, human oversight and incidents.
Learn more →Module · 06 / 09Spot checks and gap assessments, answered in the app or through a portal, frozen on the day.
Learn more →Module · 07 / 09Head office and subsidiaries: shared users, suppliers and KPIs, and one Group Compliance view.
Learn more →Module · 08 / 09Publish policies to your staff and track who read and acknowledged them.
Learn more →Module · 09 / 09Scanner results grouped into one issue per vulnerability, with an owner and a due date.
Learn more →Integrations
Connectors bring live evidence into your controls. API keys let your own systems push data in, and we build new connectors on request.
Animation: a robot arm takes data from Microsoft Entra ID, Microsoft Defender, Azure, AWS, GitHub and Google Workspace and puts it on a belt into your workspace in Acuna GRC, where your evidence, KPIs and security alerts stay current.
Entra ID Okta
 Google Workspace
 JumpCloudDefender
 CrowdStrike
 Intune
 Jamf ProAWS
 Azure
 Google Cloud
 Microsoft 365GitHub
 GitLab
 Personio
 KnowBe4
 Acronis
Connectors pull security data on a schedule, and API keys let your own systems push data in. Every call is logged.
We design the integration around your setup. Every native connector we have exists because a client needed it.
Tasks sync both ways with Jira and ServiceNow.
Meet Aiko
Aiko is the AI assistant inside Acuna GRC. It prepares real compliance work, with a reason and a source for every step, and it follows the same access rules as everyone else.
Suggest only: Aiko explains how. You do it. Ask me first (default): Aiko prepares it. You confirm. Do it and tell me: Aiko does it and shows you what it did.
Admins set the highest mode for each action. Changing a risk score, work done for someone else, more than 3 changes at once or 30 in an hour, and anything after Aiko has read supplier, web, privacy request or group data in the same chat always ask first.
Every Aiko action goes into the Activity log, kept for 12 months, with search and date filters. When someone asks why, you can show them.
Our experts
Aiko's modes set how much the software does. The Service Dial sets how much these experts do. You choose both.

Cyber security and governance consultant with 20+ years advising multinationals, governments and international organizations.

Henri Haenni
Business continuity and information security expert, certified international trainer and lecturer at Sorbonne University Paris 1.
Laura Menetrey
Strategic legal advisor in data protection and privacy law, helping organizations navigate GDPR, NIS2, DORA and the Swiss FADP.
Jean Munyarugerero
Hands-on IS and business continuity trainer and auditor with experience spanning finance, cloud, public sector and NGOs.
Jean-Emmanuel Rodriguez
Supports clients through vendor risk, compliance technology integration and gap analysis, from policy development to go-live.
Bénédicte Sévin
Leads end-to-end project supervision across implementations, audits and compliance programs for global organizations.
Your data, your choice
Pricing
No per-seat licensing, so your whole team can work in it. Start with Acuna GRC and Aiko, then add modules or our experts when you need them.
Professional
The Acuna GRC core, for organizations running advanced GRC programs.
Organization-based pricing starts from
CHF 6'390
per year
Add-on modules
Enterprise
For large organizations with complex, multi-entity GRC programs.
Price on request
For partners
MSSP
For companies that manage multiple clients.
Price on request
Request a demoSpecial pricing
We offer custom discounted rates for registered non-profit organizations, international NGOs, and accredited academic or research institutions. Eligibility is confirmed on request: usually a registration document or .edu / .ac domain is enough.
Request a demoNo commitment required.
Who is eligible
FAQ
Acuna GRC is an all-in-one governance, risk and compliance platform built in Switzerland. Its AI assistant, Aiko, does compliance work with your team one step at a time, in the mode each team chooses, and Swiss experts add extra hands when you need them.
Aiko links controls, measures, requirements and documents with a reason for each link, checks whether a risk is still rated right against its evidence, plans missing links across your library in bulk runs, drafts supplier answers from their documents, and answers questions about your group and your AI systems.
Only as far as you allow. Each team chooses a mode: Suggest only, Ask me first (the default) or Do it and tell me, and admins set the highest mode for each action. Some actions always ask first, such as changing a risk score or making more than 3 changes at once.
No. Aiko can be switched on or off, and you decide how much it does.
More than 50, including ISO 27001, NIS2, DORA, SOC 2, GDPR, the Swiss FADP and NIST CSF. A control built once counts for every framework that requires it.
Yes. The AI Governance module keeps an inventory of your AI systems and shows what is missing for conformity.
Yes. With Group management, a head office shares users, suppliers and KPIs with its subsidiaries and sees them all in one Group Compliance view.
Yes. The Trust Center module drafts answers from your approved answers library, and a person reviews each one.
In Switzerland, the EU or the US, as you choose. More detail is in our Trust Center.
Yes. Every Aiko action is recorded in the Activity log for 12 months, and every link or proposal shows its reason and source.
No. Aiko follows the same access rules as the rest of Acuna GRC, including scopes and tags. When it can't confirm what you may see, it stops and says so.
Yes, Acuna GRC is ISO 27001 certified.
More than 100 connectors bring live evidence from tools such as Entra ID, Okta, AWS, Azure and GitHub. API keys let your own systems push data in, and we build new connectors on request.
Organization-based pricing starts from CHF 6'390 per year for the Acuna GRC core, with no per-seat licensing. You add modules or expert days when you need them.
Each core subscription includes a dedicated advisor and one month of hypercare to get you set up.
Yes, as much as you want. Our Swiss experts add extra hands to keep you compliant all year: work with them (Done with you) or let them run the program day to day (Done for you). Or do it yourself with the platform.
No. Our experts help you prepare, and your certification audit stays independent.
No. Aiko helps your team with the work, our experts add hands when you need them, and your people make the decisions.
Acuna GRC is built for the people who answer for security and compliance: CISOs and security leads, DPOs, compliance officers, risk managers, IT managers who carry security on top of their job, and internal auditors. It fits startups preparing their first audit, mid-market companies with a small team, and enterprises and groups with several entities. MSSPs and consultants use it to run compliance programs for their clients.
Show us one framework or one disorganized control library. We'll show you Aiko working on it, and you decide what it applies.