| Target market | Fast-growing companies closing enterprise deals, regulated EU and Swiss enterprises under NIS2, DORA and FINMA, groups with subsidiaries, MSSPs and consultancies, organizations that want the full cycle run with experts | Startups, mid-market companies and enterprises, from a first SOC 2 to a unified view of compliance, security and trust workflows[1] | BothBoth serve growing companies; Acuna GRC also fits EU and Swiss regulated groups and MSSPs |
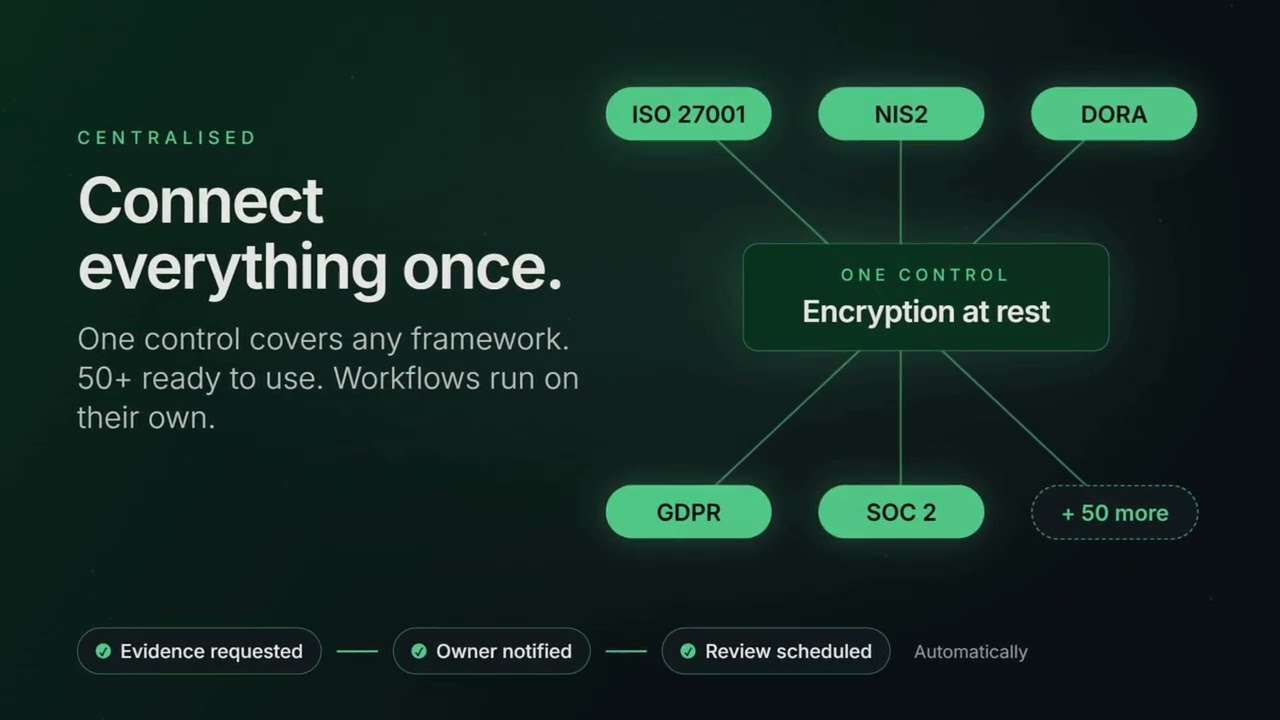
| Frameworks | 50+ in the library, all included in Core GRC: NIS2, DORA, FINMA, Swiss FADP, GDPR, EU AI Act, ISO 27001, ISO 42001, SOC 2; shared measures and controls; custom frameworks by CSV | 35+ on its list, including SOC 2, ISO 27001, NIS 2, DORA, GDPR, the EU AI Act, ISO 42001, FedRAMP, CMMC 2.0, HITRUST CSF, Essential Eight and CPS 234; custom frameworks; Essentials includes one framework[3][2] | DependsAcuna GRC for Swiss law in one shared library; Vanta for US federal and Australia |
| Hosting and deployment | Hosting in Switzerland or the EU, as the customer chooses; private cloud or on-premises | Regional hosting in the US, the EU or Australia[4] | BothBoth host in the EU; Acuna GRC adds Switzerland and on-premises |
| Controls, evidence and integrations | Connectors record control passes and fails and KPI values every 4 hours; 100+ connectors, and new ones built on request around your stack; Jira and ServiceNow two-way task sync; API v1, webhooks, scheduled CSV imports | Automation and continuous monitoring; data pulled automatically from "400+ tools"; Vanta API[1] | DependsVanta: larger ready-made catalog; Acuna GRC: connectors built to your stack |
| AI architecture | Aiko is native to the platform and works on one data model (requirements, measures, controls, risks, suppliers, evidence): it answers, drafts tasks and KPIs, links records in bulk runs and proposes risk scores from their evidence; a person confirms under the policy an administrator sets; AI can be switched off and the platform keeps working | Vanta AI and the Vanta Agent, which drafts policies, completes questionnaires and calls out issues; an Agent for TPRM[1] | Acuna GRCNative to one data model, under your policy |
| AI governance | AI Governance module, available now: register of AI systems, impact assessments, human oversight, incidents and a contestation channel; EU AI Act and ISO 42001 in the library | Work toward ISO 42001, the EU AI Act and NIST AI RMF with AI policies, use cases and impact assessments, varying by plan; AI inventory and guardrails coming soon as a separate, paid solution[5] | BothBoth cover it; the Acuna GRC register and oversight are live today |
| Third-party risk (TPRM) | Supplier Shield: supplier register with your own exposure model, questionnaires by campaign through a supplier portal, a 1 to 3 shield rating, a daily A to F OSINT grade, and Aiko drafting or evaluating answers for a person to confirm | Third Party Risk Management: vendor onboarding and security reviews in one place, with Vanta’s Agent for TPRM[1] | BothBoth run TPRM; Acuna GRC keeps it on the same records as your controls |
| Trust Center and questionnaires | Trust Center: public trust page with open and gated tiers, gated documents behind an NDA signature, questionnaire answers drafted only from approved library facts, each showing what it was built from, and a log of every view and download | Trust Center to show compliance status and documentation; AI questionnaire automation, 25 a year on Plus and 144 on Professional[1][2] | BothBoth cover it; Acuna GRC answers from the same records as your program |
| Pricing model | Published: from CHF 6'390 per year, per organization, no per-seat fees; all 50+ frameworks, Aiko and 100+ connectors included; add-on modules and services priced in the same offer | Four plans (Essentials, Plus, Professional, Enterprise) without published prices; personalized pricing after a demo; several features marked as add-ons[2] | Acuna GRCPrice you can see |
| Services by experts | Dedicated advisor and one month of hypercare included; co-managed or fully managed; CISO and DPO as a service with a named Swiss expert; in-house certified lead auditors | Audit partners and an auditor directory; solution and service providers in its partner program[6] | Acuna GRCSwiss experts in house, up to CISO and DPO roles |
| Groups, MSSPs and partners | Group management for a head office and its subsidiaries, with a Group Compliance dashboard; each MSSP client in its own organization, white label under your brand | Multi-organization workspaces and MSP-managed accounts; solution providers resell and deliver services[4][6] | BothBoth handle several organizations; Acuna GRC adds a group view and white label |









 Okta
 Google Workspace
 Defender
 CrowdStrike
 AWS
 Azure
 GitHub
 Jira